INVITE-ONLY EXECUTIVE ROUNDTABLE
Agentic DevSecOps in a Regulated Enterprise
From AI-generated code to enterprise accountability, are your controls keeping pace?
📅 Tuesday, 10 November 2026
⏰ 12:00 PM – 2:00 PM
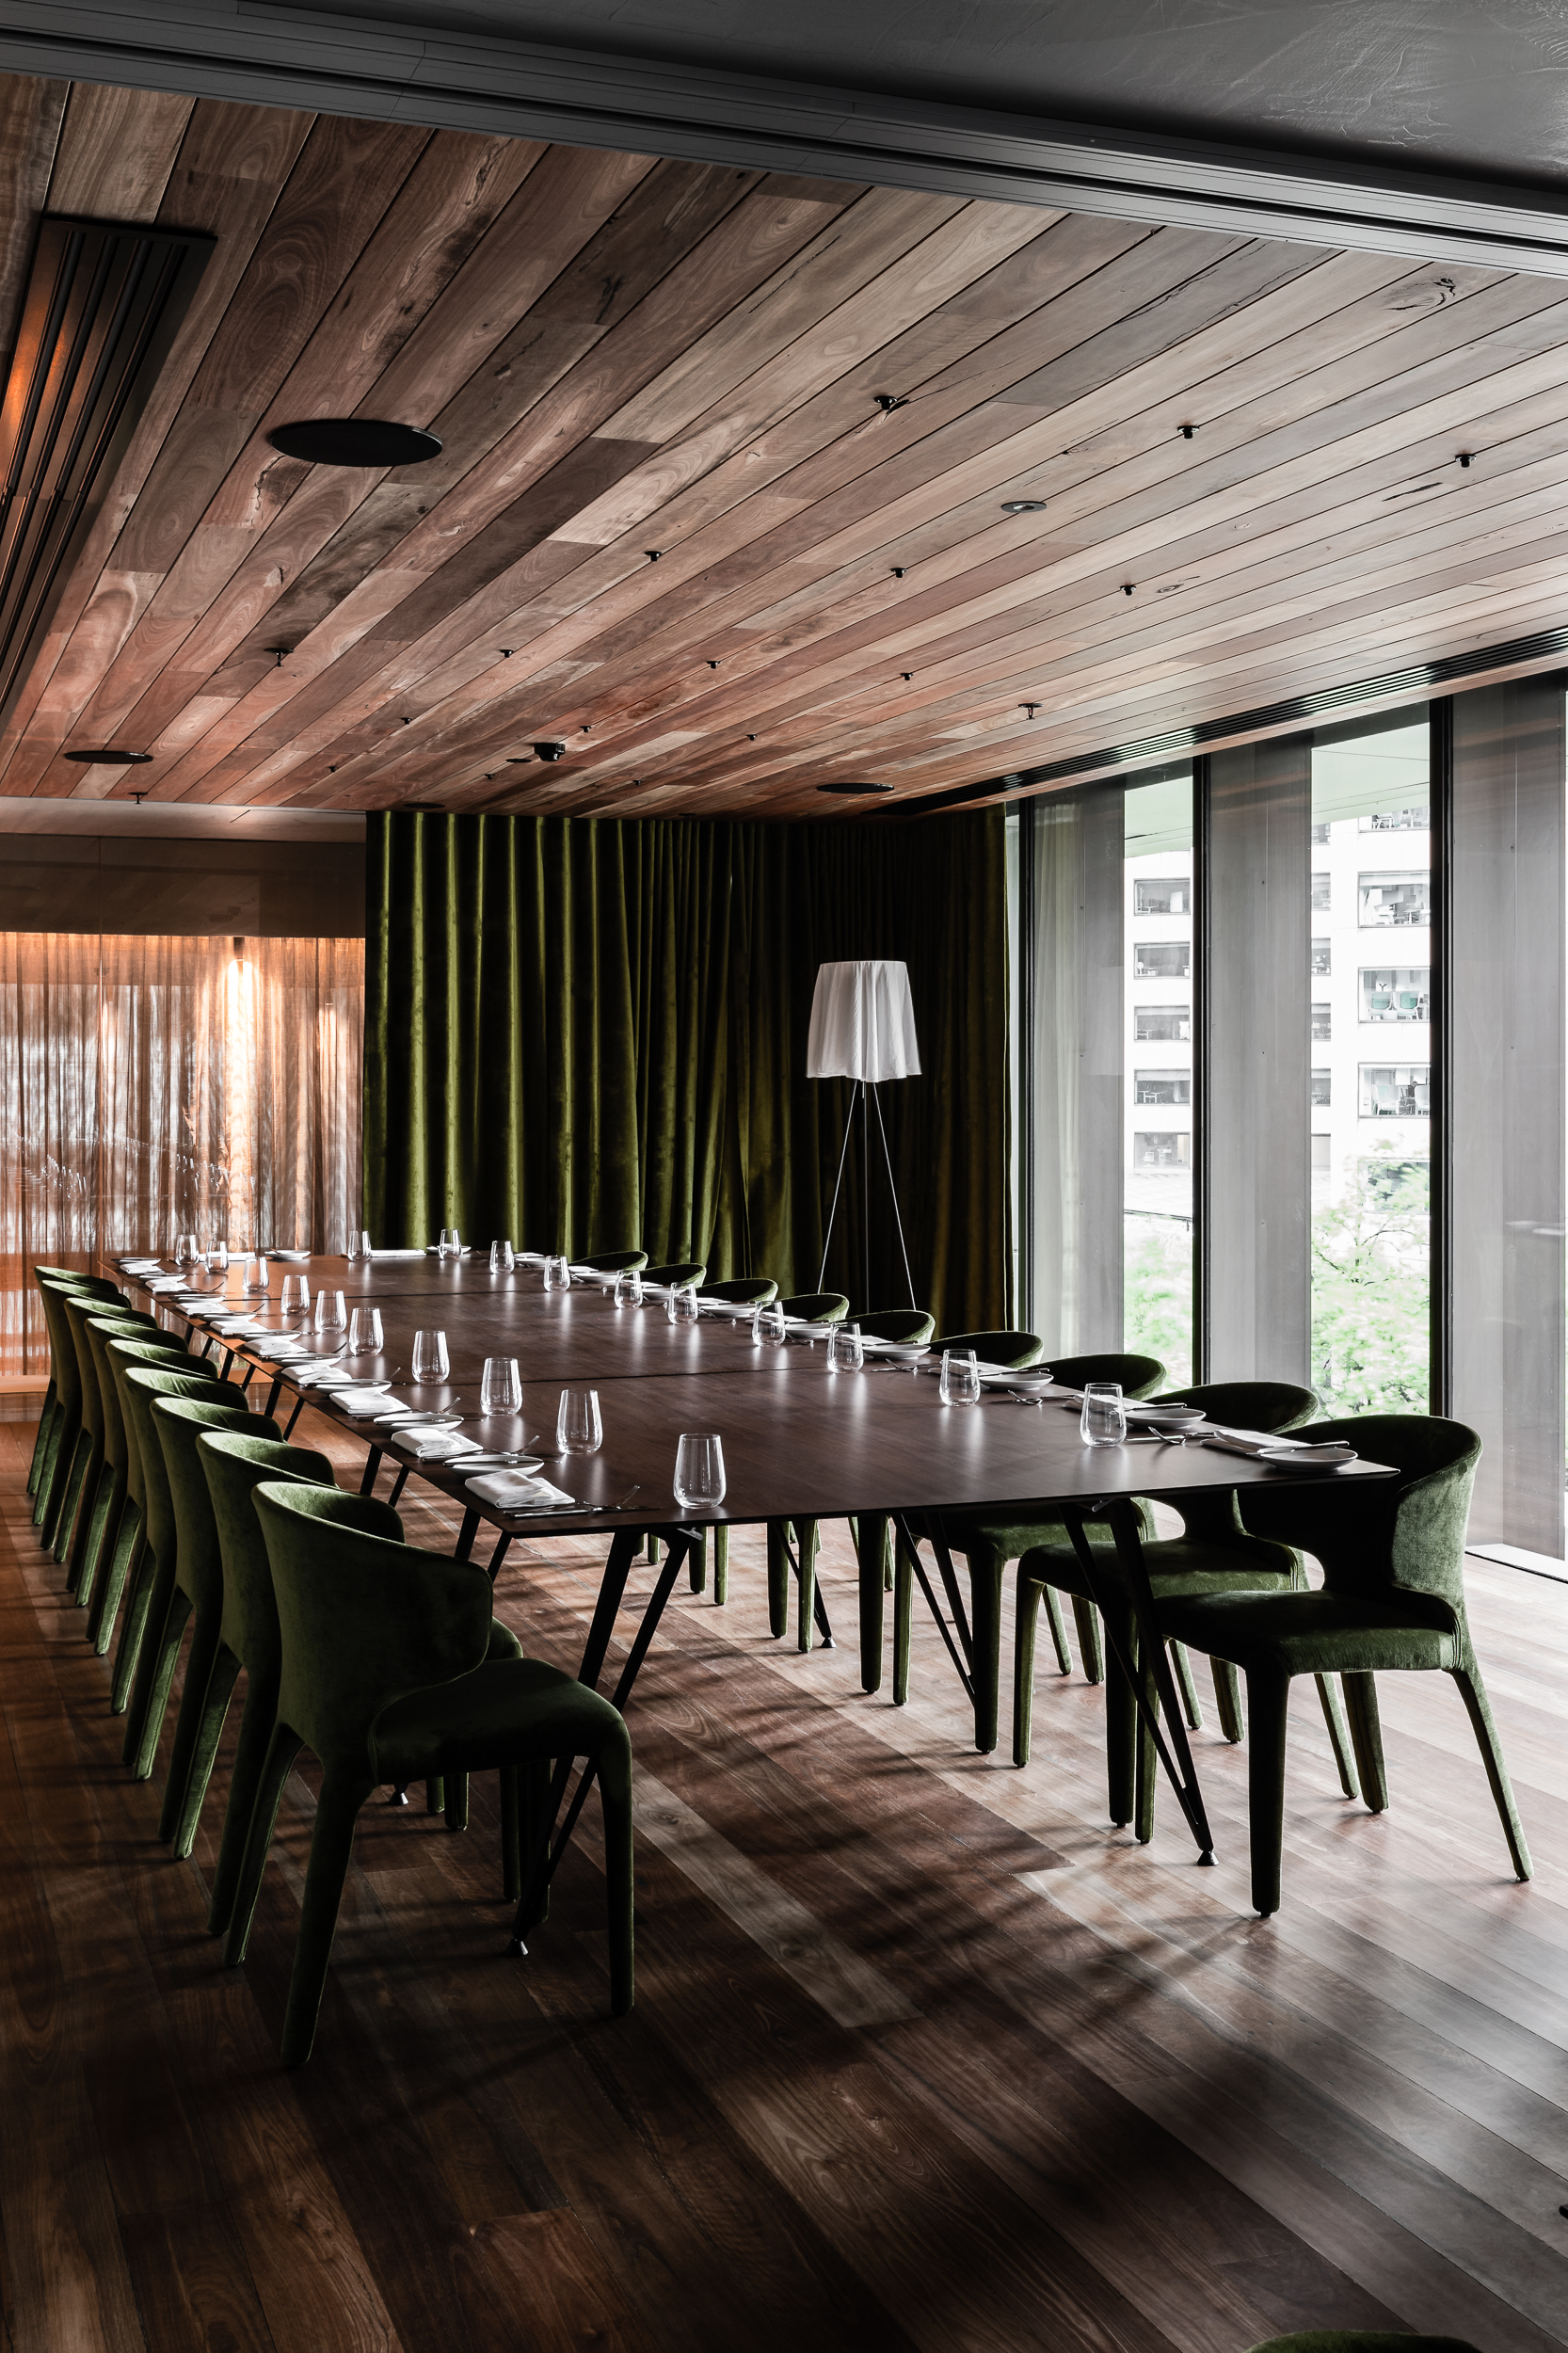
📍 Society Restaurant, 80 Collins St, Melbourne
Whether driven by regulatory obligations, customer trust, operational resilience or board-level governance expectations, organisations are being challenged to demonstrate control over increasingly autonomous software delivery processes.
AI is changing how software gets built. Development teams are already using AI agents to write code, generate tests, review pull requests and automate remediation. At the same time, boards, customers, auditors and regulators are demanding greater transparency into how software is created, secured and governed.
The question isn't whether AI becomes part of the development lifecycle. It's how you maintain accountability, auditability and trust when software is increasingly created and managed by autonomous systems.
Held under Chatham House Rule. What's said in the room stays in the room, so the conversation can be direct.
-
![]()
10 NOV 2026
-
![]()
12:00 PM – 2:00 PM
-
![]()
Society Restaurant, 80 Collins St


WHY THIS MATTERS NOW
The questions organisations are being asked are changing
Whether the scrutiny comes from regulators, auditors, boards, customers or internal risk teams, organisations are increasingly expected to demonstrate accountability, visibility and control over AI-assisted software development.
That's already playing out in regulatory guidance, APRA and ASIC have both issued strongly worded direction on AI use, with a specific focus on the risk introduced when AI writes code. Neither is legislation yet, both are a clear signal of where scrutiny is heading, alongside emerging obligations under the SOCI Act and comparable requirements overseas.
Expect a direct conversation with peers navigating the same shift, not a product pitch.
Development teams are already using AI agents to write, test and review code, often faster than governance processes have adapted to.
When an AI agent contributes to a change that causes an incident, accountability doesn't automatically follow, it has to be designed in.
Most organisations can't yet say, with evidence rather than assumption, exactly what's running in production.
Segregation of duties, built for human-only development, doesn't automatically hold up in an agent-driven SDLC.
The gap between "we have controls" and "we can prove they worked" is where operational, reputational and regulatory risk actually lives.
WHAT THIS DISCUSSION WILL COVER
Four areas the room will work through together
1. Where accountability sits
When AI agents write, review and deploy code, who's actually accountable when something goes wrong, and how that answer changes as agents take on more of the workflow.
2. Segregation of duties in an agent-driven SDLC
How a control built for human-only development teams needs to evolve when some of those "team members" are autonomous.
3. What's actually running in production
How mature your software supply chain visibility really is, and whether you could identify affected components within hours of a critical vulnerability, not days.
4. Evidence over assumption
What it actually takes to give a regulator or auditor a evidence-based answer, rather than a confident one, when they ask what's running and why it's trusted.
WHAT YOU’LL TAKE AWAY
Leave with more than notes
A clearer view of where accountability actually breaks down
How governance built for human-only development holds up, or doesn't, once AI agents are writing and reviewing code.
A sharper read on where scrutiny is heading
What regulators, boards, and customers are increasingly expecting organisations to demonstrate about AI-assisted software delivery.
Perspectives from peers
How other regulated organisations are actually approaching software supply chain visibility and evidence-based governance.
A benchmark for your own maturity
How your organisation's software supply chain visibility compares with peers facing the same regulatory pressure.
A sense of what "audit-ready" actually requires
Beyond having controls on paper, what it takes to prove they worked when a regulator asks.
WHO WILL BE IN THE ROOM
A curated group of senior security and technology leaders
The value of this discussion comes from hearing how peers from highly regulated and digitally-led organisations are actually approaching the shift to AI-assisted software delivery, not from a single point of view.
Drawn from across Australia's most regulated and digitally advanced sectors, including:
Security Leadership
CISO · Principal Security Architect
Application Security & Engineering
Director of Application Security · Director of Application Engineering · Director of Security Engineering
DevSecOps & Platforms
DevSecOps Director · GM, Platforms and Engineering
Participants are selected to ensure a high-calibre, peer-level discussion, held under Chatham House Rule.
The Programme
12:00 PM: Arrival and networking
A chance to meet the room before the discussion starts
12:15 PM: Welcome and discussion framing
Setting the scope and ground rules for the conversation ahead
12:20 PM: Setting the scene
The discussion will open with trends from across the industry
12:35 PM: Entrée & discussion, where accountability sits
The room's first course, paired with the day's opening discussion area
1:00 PM: Mains & discussion, segregation of duties
Continuing over the main course, extending into what's actually running in production. Moderated by Vanessa Kyte, OpenText
1:30 PM: Dessert & discussion, evidence over assumption
The final discussion area, closing out the working part of the lunch
1:50 PM: Closing reflections and key takeaways
Pulling the threads of the discussion together.
2:00 PM: Close
Attendees are welcome to stay on for informal discussion..
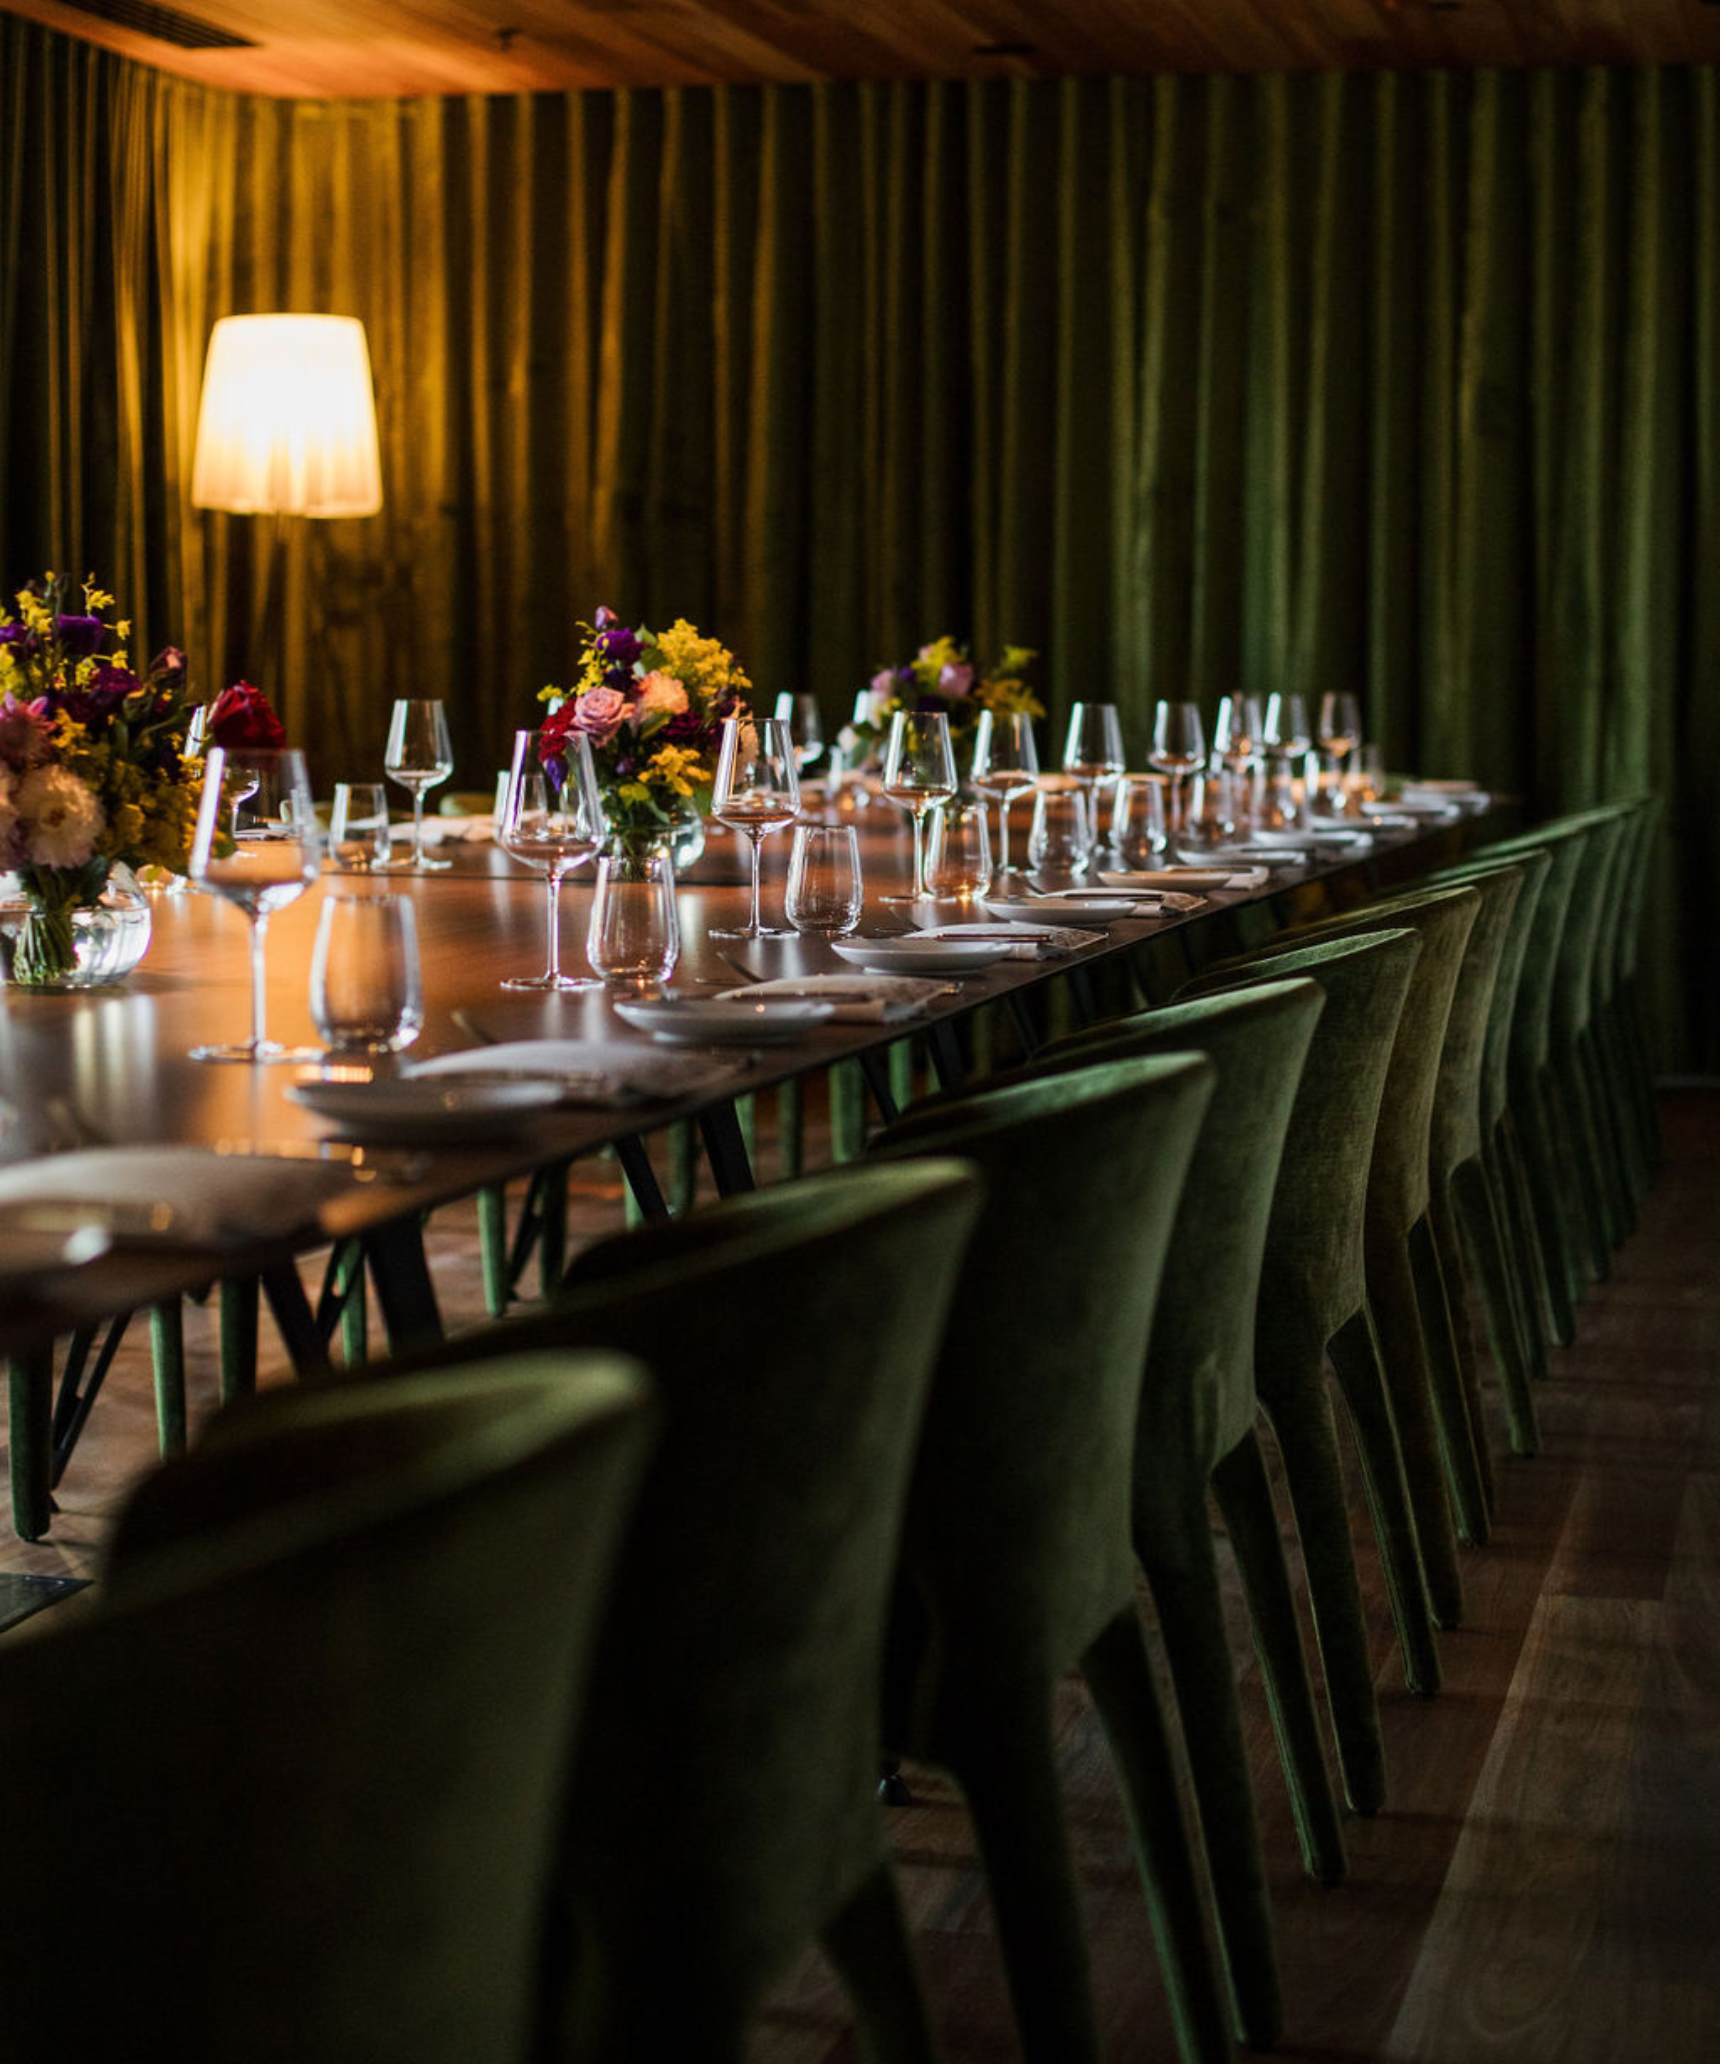
The conversation is accompanied by lunch at Society, Chris Lucas's dining room at 80 Collins Street in the heart of Melbourne's CBD.
Entrée, mains and dessert are woven through the discussion itself, giving the room a natural rhythm rather than a formal agenda.
Reserve Your Seat
Participation is limited to a select group of senior security, engineering and risk leaders to ensure a high-quality, peer-level discussion.
If you're responsible for application security, software delivery, cyber risk or regulatory compliance within a regulated or critical infrastructure organisation, this discussion will be directly relevant.
To maintain the integrity of the discussion, we ask that confirmed participants make every effort to attend, or provide advance notice should their availability change.
📅 Date: Tuesday, 10 November 2026
⏰ Time: 12:00 PM – 2:00 PM AEST
📍 Location: Society Restaurant, 80 Collins St, Melbourne